
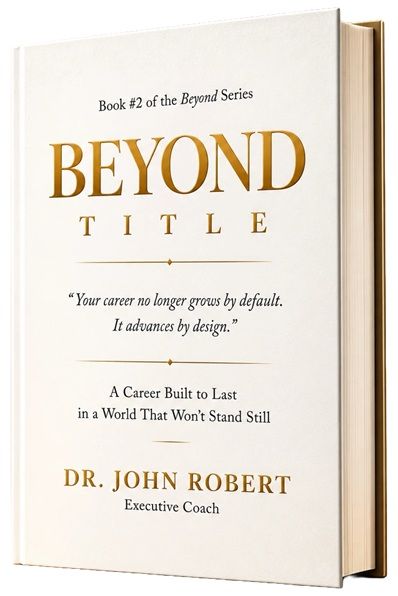
Dr. John Robert’s Beyond Title is not a security book. That is exactly why every security leader in India should read it.
By GB Singh, Editor-in-Chief
Books reach this desk every month, and most I can place within a few pages. Dr. John Robert’s Beyond Title: A Career Built To Last In A World That Won’t Stand Still took me longer. It is a career book, written for the professional who has the title, the tenure and the track record, and senses that these no longer add up to what they once did. None of its case studies has a security professional as the main subject. I finished it convinced that ours is the fraternity that needs it most.
Robert’s central idea is what he calls the Experience-Relevance Gap, the distance between what a professional has built up over the years and what the market now wants and recognises. He breaks it into three parts. Capability is what you can do against what is now required. Currency is how recently you learnt it. Visibility is where your ability is known, compared with where decisions about you are actually taken. The gap, he argues, widens quietly inside careers that look strong, and shows itself at the worst possible moment.
Read that third dimension as a security leader and it lands hard. In most professions, good work leaves evidence. In ours, it is a non-event. The perimeter held, the crowd dispersed safely, and nobody outside the control room knew how close it came. Robert observes that capability nobody can see is a private asset the market cannot invest in. For our people that privacy is doubled: first because the work prevents rather than produces, and second because whatever credit it does earn rarely travels beyond one organisation’s walls.
Two of his case studies could have been written about people I know. Fatima, a Dubai operations head with eighteen years of crises resolved, is passed over for the COO’s chair because the board sees her as the person who keeps the current operation running. Her identity, Robert writes, had been “written for her, one operational crisis at a time.” Nadia, who built a UAE bank’s risk function, was known as the person who said no. Given ninety days by her CEO, she stopped calling her function risk management and started calling it strategic risk intelligence. Within a year, risk was being brought in at the strategy stage rather than the approval stage. Her title did not change. How she was seen did.
I have seen too many boardrooms call in the security head after the decision, to protect what others have already chosen. Nadia’s ninety days are the most practical pages in this book for any CSO who wants to be in the room earlier.
There is a second, more Indian reading. Many of our senior security leaders arrive in the corporate world on a second career, after years in uniform. Robert’s three-stage model of Building, Leading and Contributing treats each move as a redesign, not a continuation. Fittingly, the Foreword is by Dr. Anuraag Guglaani, an NDA graduate and trained fighter pilot, who recalls that in military training a plan is never finished; it is revisited as the terrain changes. Too many of us apply that discipline to operations, never to our own careers.
The story of Sameer and Vatsala, two senior colleagues in the same Gurgaon consulting firm, makes the point without mercy. Sameer gave the firm twenty-three loyal years and, after a restructuring, spent seventeen months looking for work. Vatsala had spent the previous three years building a board seat at a Bengaluru fintech, a think-tank panel in New Delhi and a quarterly newsletter alongside her day job. For her, the restructuring was an inconvenience, not an ending. Any CSO eyeing advisory work after retirement should study that contrast.
Equally uncomfortable is Rahul, a seasoned risk head who cannot explain a new data model to a committee and defers to the data science lead beside him. Anyone who has handed the microphone to the IT team on video analytics will wince.
My one hope for the next edition would be to see more of India reflected in its pages. Much of the research and many of the examples Robert draws upon are American. Given his own beginnings in public service in a newly liberalising India, he is particularly well placed to bring more Indian experiences and case studies into the narrative. Readers should also be prepared for a book rich in frameworks, from ENGINE to RPI. These are not concepts to be skimmed over; they deserve time and reflection to fully appreciate their value.
Start, though, at the back. The seven-question self-assessment there takes minutes; I urge every reader to attempt it honestly, answering as the market sees you and not as you see yourself.
Then ask the question Robert places at the heart of the book: when your name comes up in a room you are not in, what do people say? In a profession where the best day is the one on which nothing happens, it may be the most important security question you will ever answer.
Disclosure: This review was commissioned by the author. The opinions expressed are the editor’s own