
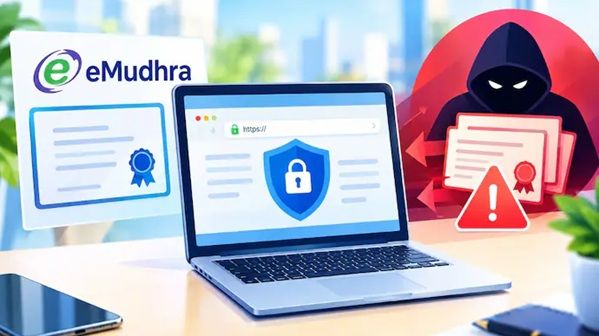
India’s cybersecurity agency CERT-In has issued an advisory warning about a security compromise involving eight intermediate digital certificate authorities linked to Indian company eMudhra. The flaw could allow attackers to create fake security certificates for websites they do not control, potentially enabling them to impersonate legitimate websites or interfere with encrypted internet communications.
In its advisory dated October 21, CERT-In said the affected private cryptographic keys were generated with insufficient randomness, making them vulnerable to recovery. The agency has recommended security updates, checks for affected certificates and changes to certificate trust settings to reduce the risk. The incident involves TLS certificates, which play an important role in securing websites and protecting information exchanged between users and online services.
CERT-In has recommended several steps for organisations, IT administrators and users whose devices or services may rely on the affected certificates.
-Update browsers and software: Install the latest security updates for Firefox, Firefox ESR and other affected browsers, applications and operating systems.
-Update certificate trust stores: Ensure devices, servers and applications receive the latest certificate revocation and distrust information from their respective vendors.
-Check certificate dependencies: Identify websites, applications and services that rely on the affected intermediate CAs or the eSign ECC Root CA – G3 certificate.
-Replace affected certificates: Obtain replacement TLS certificates from a trusted, unaffected certificate authority where necessary. Administrators should also replace otherwise legitimate certificates that will no longer be trusted by relevant clients.
-Verify TLS certificates: Check certificate chains, issuing authorities, validity periods and revocation status. CERT-In has also advised against bypassing certificate-validation warnings or disabling certificate verification.
For ordinary users, keeping browsers and operating systems updated is an important first step. Organisations that manage websites, servers or enterprise applications should also check whether their systems depend on the affected certificates and take corrective action where required.