
Modern software is constantly telling us what is happening.
For years, security teams have had to make trade-offs around telemetry filtering high-volume sources, sampling data and limiting retention because storing and analysing massive volumes of data was prohibitively expensive. But with AI increasingly capable of investigating across multiple datasets, time periods and hypotheses, the value of retaining that underlying data is changing. The article argues that AI is only as powerful as the evidence available to it. If identity logs, network activity or application telemetry were discarded months ago, even the most advanced AI investigator cannot reconstruct that missing context. This has implications for how enterprises think about detection, investigation and incident response.
Every login, API call, process, transaction, configuration change, network connection and
application error leaves behind a signal. Taken together, these signals can tell us how a system is behaving, where risk is building, and sometimes even where an attack began.
The problem is that enterprises have spent years learning not to keep all of it.
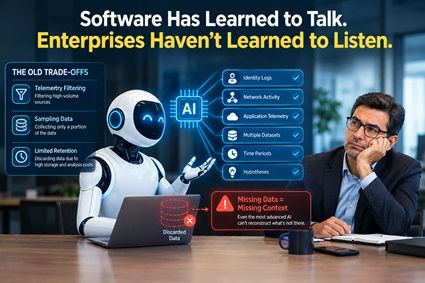 Security teams have been forced to make choices about what data is worth collecting, how much of it to retain, and how long to keep it. High-volume sources are often filtered. Some telemetry is sampled. Detailed data may only be retained for a short period. This is not because the information has no value. It is because storing, indexing and searching very large volumes of telemetry has traditionally been expensive.
Over time, an infrastructure limitation started to look like a data strategy.We began to accept that collecting less data was the smarter approach. Security investigations show why that assumption can be dangerous.
Imagine an employee account is found to be compromised today. The obvious question is not just what that account did in the last 24 hours. Investigators may need to know where it authenticated from three months ago, whether its access patterns changed, which applications it touched, whether privileges were modified, and whether the same device or IP address appeared elsewhere.
An authentication event that looked completely normal when it happened can become important months later.
The same problem appears in ransomware investigations. An endpoint alert may only be the final visible stage of an attack. Investigators may need to connect DNS activity, identity events, firewall logs, process activity, cloud access and application telemetry to understand how the attacker entered, moved through the environment and reached critical systems. If some of that data was filtered out or aged out, the investigation begins with gaps.
Data exfiltration is another example. A large transfer on its own may not mean much. But the picture changes when it follows an unusual login, a privilege escalation and repeated access to sensitive files. No single event tells the whole story. The value comes from being able to connect events across systems and across time. This is where AI changes the discussion.
Until recently, there was a practical limit to how much data a human analyst could examine. Collecting everything did not automatically mean someone could understand everything. Security teams built dashboards, rules and alerts to reduce enormous streams of telemetry into something people could manage. AI gives us another way to work.
An AI investigator can run many queries as part of a single investigation. It can search several datasets, widen or narrow time windows, test different hypotheses, compare entities and repeat searches as new evidence appears. An investigation that would require an analyst to move between several tools and manually follow each lead can increasingly be explored by software. That changes the value of the underlying data.
But there is an important limit. AI cannot reason over evidence that was never collected.
If identity logs were sampled, network telemetry discarded, or application events retained for only a few weeks, a better AI model cannot recreate them later. Intelligence can only be as complete as the evidence available to it. This is why I believe the next advantage in enterprise security will come from collecting more data, not less.
That does not mean collecting information without thought or simply creating larger data lakes. It means preserving high-fidelity telemetry across more of the enterprise and making it economical to retain, search and analyze. Security teams rarely know in advance which event will matter later. A routine cloud API call may become relevant after a new vulnerability is disclosed. A software update may need to be revisited after a supply-chain compromise is discovered. Months of access history may reveal an insider threat that no individual event could expose.The ability to go back matters.
For years, the industry has focused on reducing telemetry because the technology underneath could not economically support the volume. New storage architectures and AI change that equation.
Software has already learned to talk. The opportunity now is not simply to listen more carefully to a smaller number of signals. It is to preserve more of the conversation and give security teams and AI systems the ability to understand it.
In the AI era, having the best model may not be enough. The real advantage may belong to the enterprise that gives that model the most complete picture of what actually happened.
The author is the founder and CEO of Bloo, an enterprise telemetry data fabric and security platform. He is a highly experienced Intrusion Analyst, and has been building threat detection systems for about two decades.